
Core, plugins & themes
Wordfence advisory matching, version checks and update guidance. The feed requires a configured API key.
VULNERABILITY MONITORING, WITH DIRECTION
Outdated software can leave your websites exposed. PantauCVE helps you identify known vulnerabilities, prioritize important risks and organize remediation in one place.
For IT teams, agencies and businesses in Malaysia.
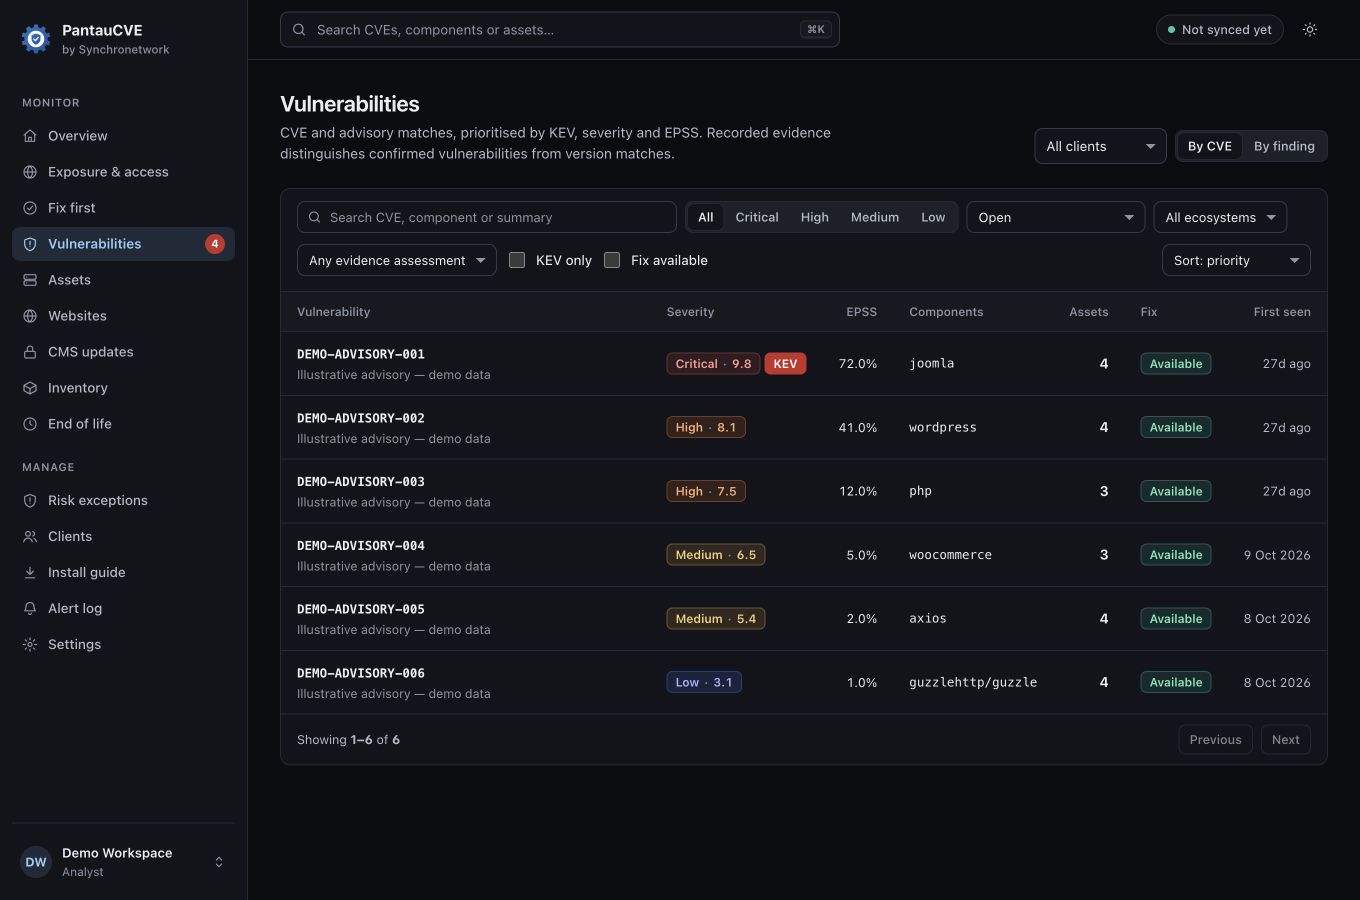
BUILT AROUND THE ENVIRONMENTS YOU MANAGE
CLARITY BEFORE ACTION
A CVE number alone does not tell you what to do. PantauCVE connects software versions, asset context and team actions so findings have a clear next step.
Bring servers, websites and software components together by client and asset.
Review CVE matches alongside KEV, EPSS and asset importance. A version match remains distinct from a confirmed CVE.
Assign owners, target dates and ticket references. Review findings again after updates.
ONE VIEW, MORE ORGANIZED ACTION
See inventory, filter findings and organize remediation without assembling reports by hand.
PANTAUCVE / 01
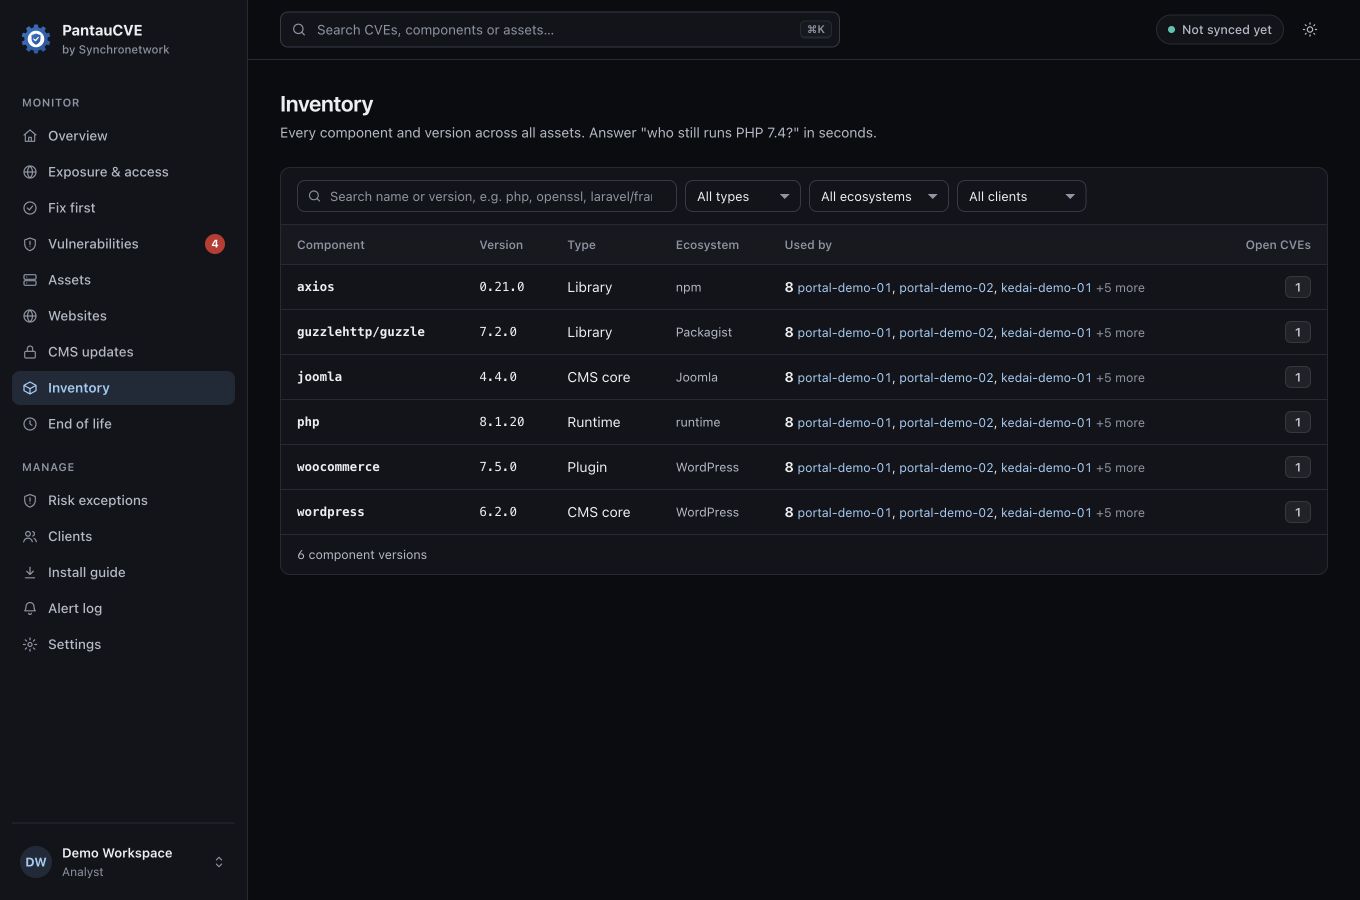
Find PHP versions, CMS components and end-of-life software across assets. Read-only agent inventory adds context that external checks cannot see.
PANTAUCVE / 02
Review the factors behind a finding’s priority. Keep service observations, advisory matches and analyst-confirmed findings distinct.
PANTAUCVE / 03
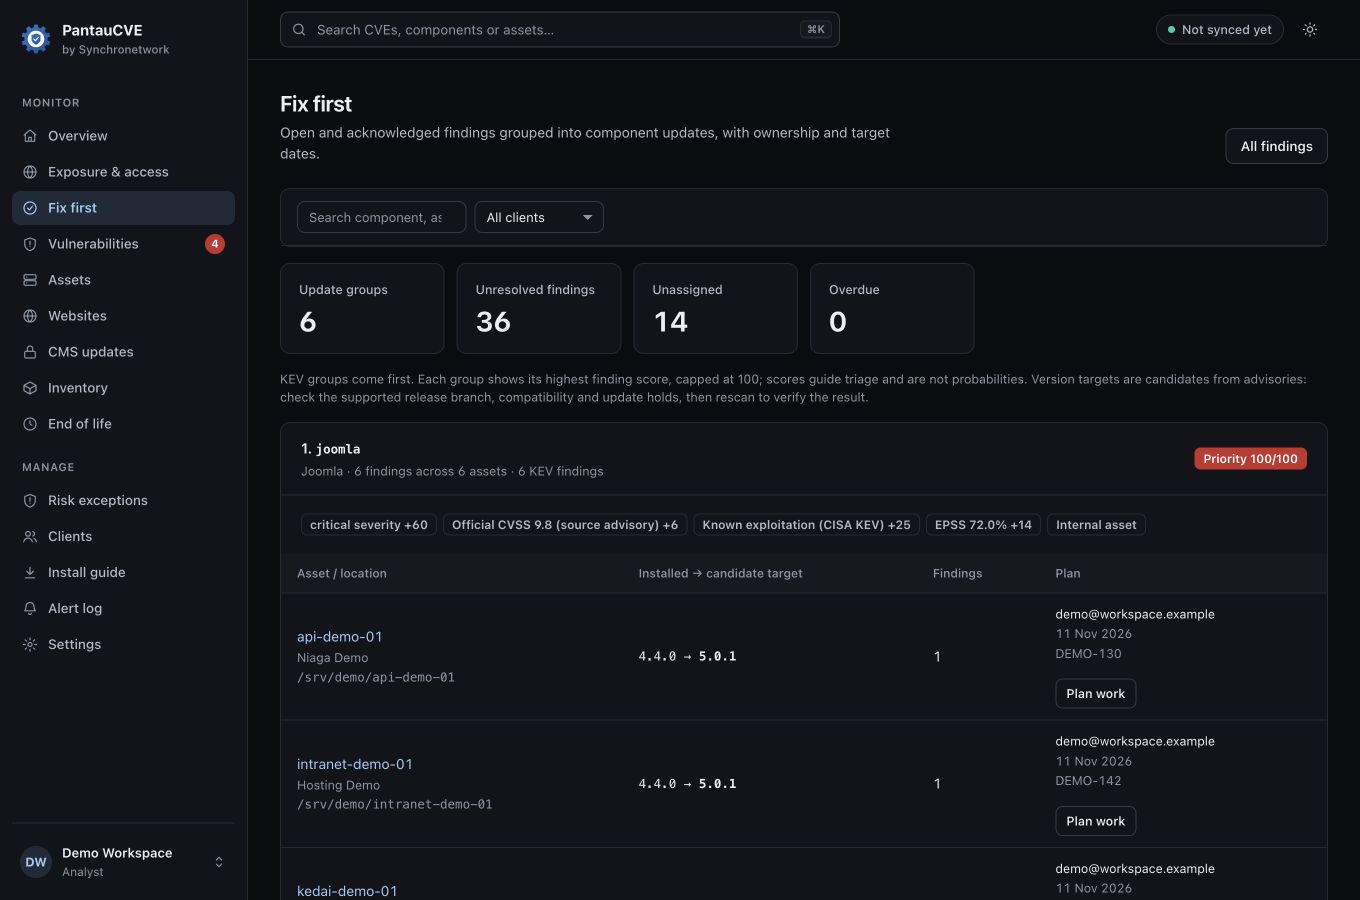
Group findings into component actions. Record accountable owners, target dates and update blockers.
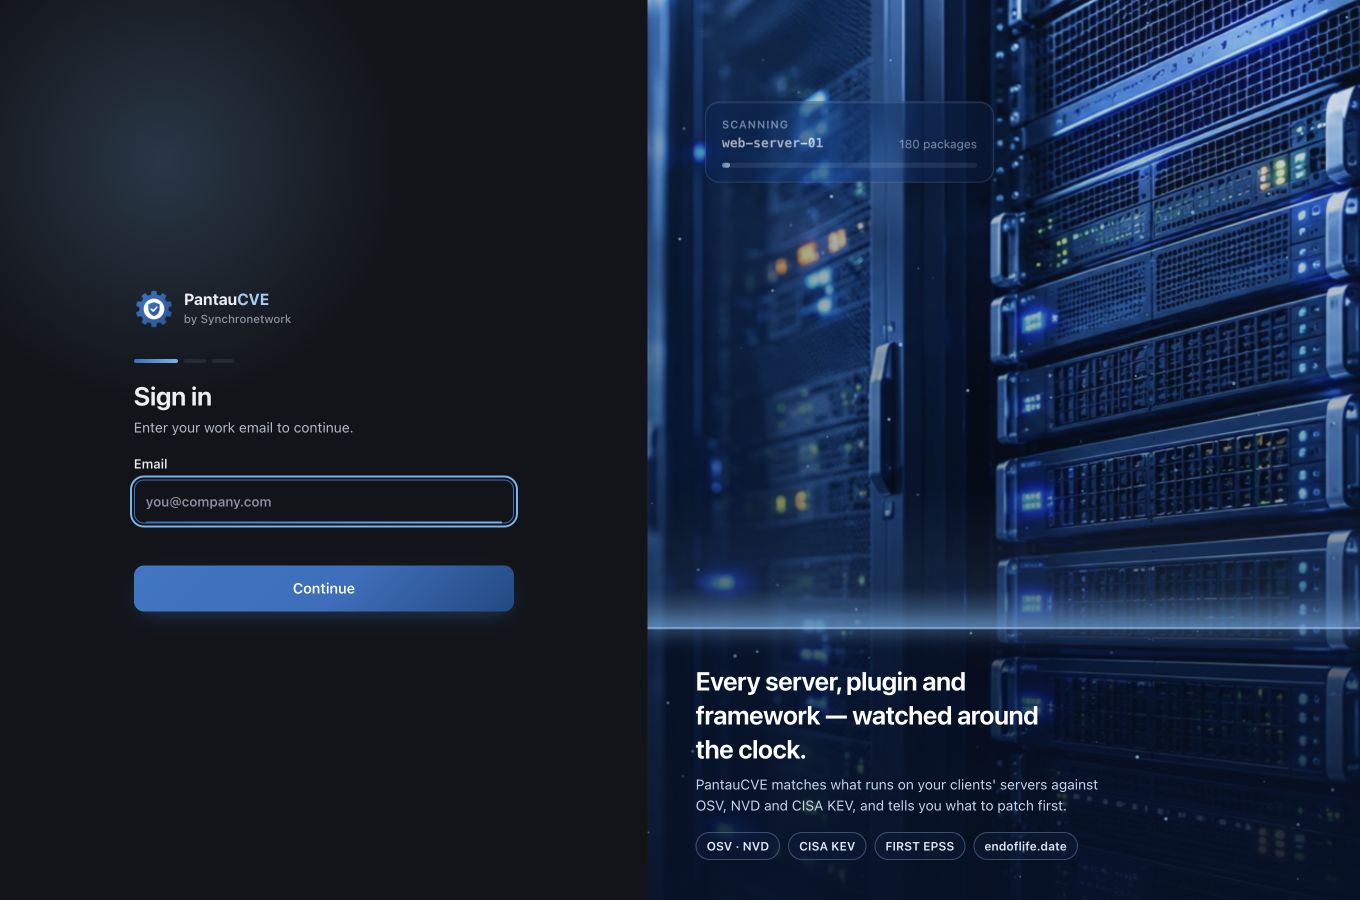
YOUR TEAM’S WORKSPACE
See the actual sign-in screen before you begin. Team roles, optional authenticator and email verification according to workspace configuration keep access deliberate.
LOCAL CONTEXT. PRACTICAL COVERAGE.
From a single portal to multi-client hosting. Choose an inventory method that fits the access you have.
Wordfence advisory matching, version checks and update guidance. The feed requires a configured API key.
Core version inventory and NVD matching. Joomla extension CVE monitoring is not yet supported.
The agent recognizes Plesk and vhost paths. Monitor server software without giving PantauCVE panel passwords.
Identify cPanel, EA-PHP and CloudLinux alt-PHP. Inventory depends on user access and authorized paths.
Read-only agent · Manual inventory · Report upload for restricted networks
FOR TEAMS KEEPING OTHER PEOPLE’S SYSTEMS RUNNING
Understand which components need attention without reading every advisory.
Business websites · e-commerceSee portal and vendor status in a shared inventory, with accountable owners and client reports.
Portals · subportals · internal systemsManage multiple clients, find recurring versions and group fixes by component.
Multi-client · servers · CMSPACKAGES THAT FIT YOUR SCOPE
Asset count, inventory methods and reporting needs shape your package. Discuss a demo to confirm the fit.
For business websites and small teams.
RM79.20/month
First month. Then RM99/month
Secure checkout with CHIP
Request a demo firstFOR MULTI-ASSET PORTFOLIOS
For web vendors and hosting operators.
RM239.20/month
First month. Then RM299/month
Secure checkout with CHIP
Request a demo firstFor portal portfolios and IT processes.
Let’s discuss
A proposal for your organization
Prices are in Malaysian Ringgit. Any displayed discount applies to the first month only. Renewal is arranged separately, with no automatic card charge. Contact us for service activation and monitoring scope.
BEFORE YOU BEGIN
CVE identifiers describe publicly known security vulnerabilities. PantauCVE matches software inventory against relevant advisories and helps teams decide what to do. Coverage depends on data sources, detected versions and configuration.
No. A version match needs context, including vendor backports and actual configuration. PantauCVE distinguishes advisory matches from analyst-confirmed CVEs. It does not guarantee detection of every vulnerability.
PantauCVE does not store hosting panel passwords. A read-only agent collects authorized inventory and submits it using an asset token. Manual inventory or report upload is available when agent installation is unsuitable.
Agent reports can be generated and uploaded manually for isolated environments. Outbound connections, proxies and deployment requirements should be assessed with your IT team during scoping.
No. It helps organize and track remediation. Your team approves and performs changes; new inventory and checks help reassess finding status.
CVE monitoring complements periodic security assessments. It does not replace pentesting, audits or guarantee compliance with any policy.
LET’S UNDERSTAND YOUR SCOPE
Tell us about your environment. Discuss how PantauCVE can help your team understand risk and organize the next steps.
PANTAUCVE / CHIP
Please wait for payment confirmation.
Contact our teamReturn to PantauCVE